

HIA Deadlines for Singapore Clinics: What Must Be Done by 1 September 2027
For many Singapore healthcare providers, 1 September 2027 is the first major Health Information Act (HIA) compliance deadline.
GPs providing Outpatient Medical Services are in the first implementation batch. By 1 September 2027, they must start contributing required health information to the National Electronic Health Record (NEHR) and implement the applicable Cybersecurity and Data Security (CS/DS) measures.
Private hospitals, clinical laboratories, radiology laboratories, and nuclear medicine services are also in this first implementation batch. Specialist outpatient clinics follow in September 2028, while outpatient dental services and several other healthcare categories follow in March 2030.
For a GP clinic, this means HIA preparation is no longer something to leave until the final months of 2027.
Your clinic may need changes to its health information system, cybersecurity controls, backup processes, user access, devices, network, and internal procedures, and some of those changes take time to assess and implement.
The practical goal: know your gaps early enough to fix them before they become deadline problems.
This guide explains what Singapore clinics should prepare for, which deadlines apply, and where Advance IT can support the technical side of HIA readiness.
HIA Deadline at a Glance
Here is the current implementation schedule published for healthcare providers:
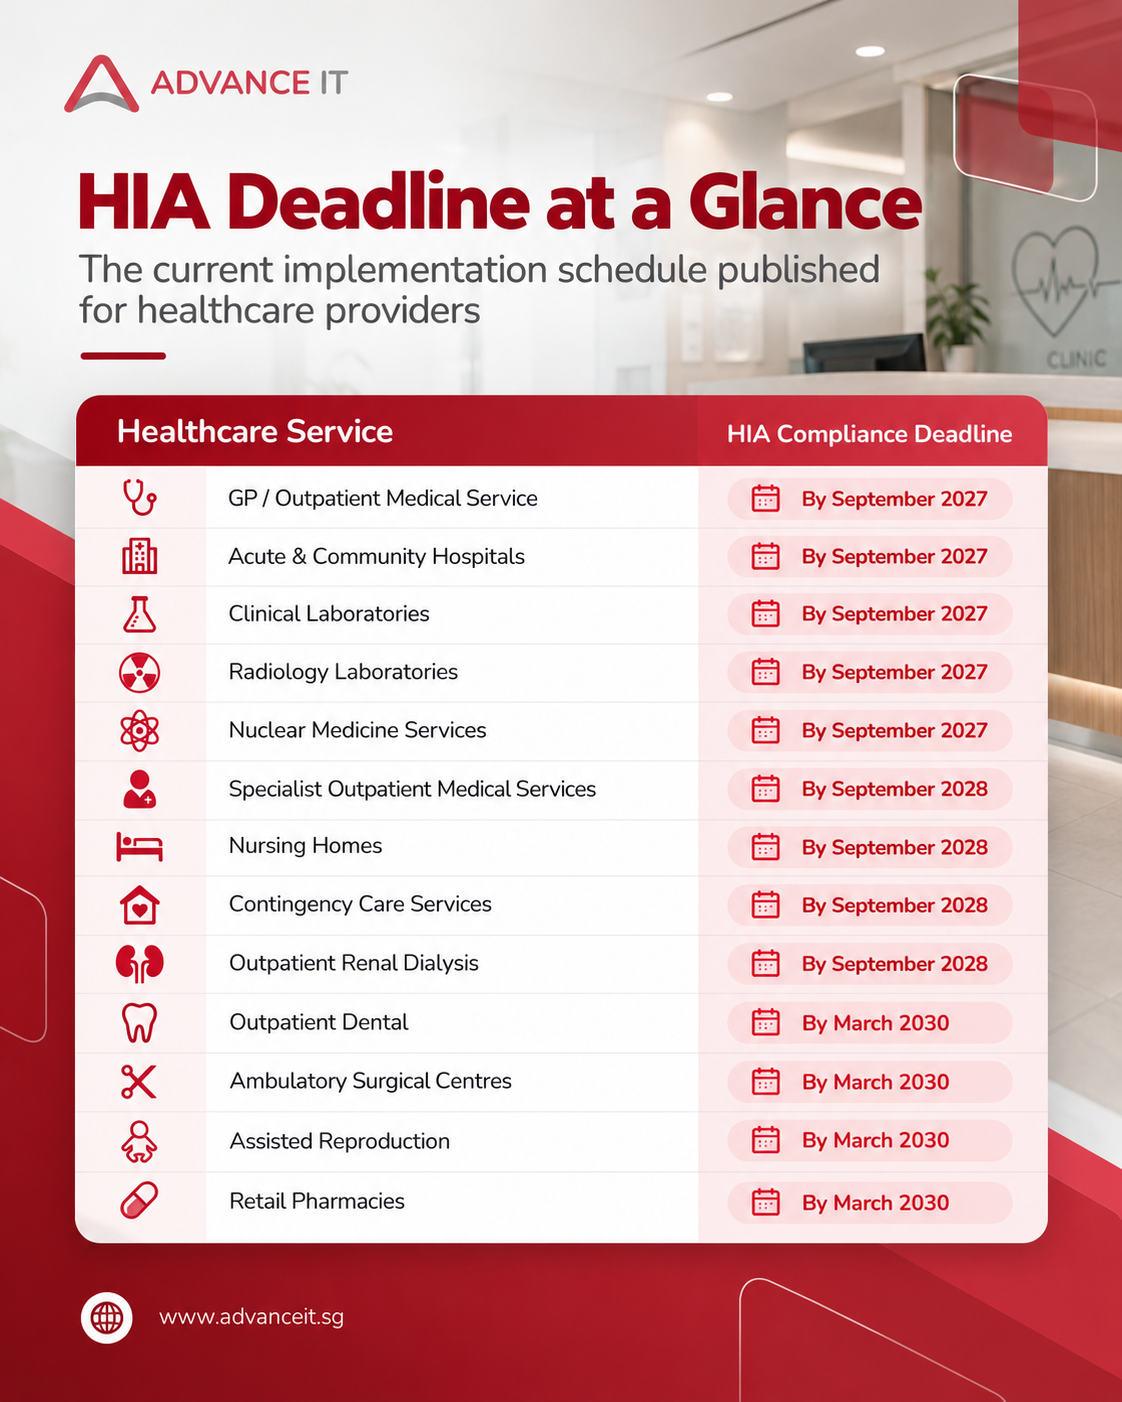
For providers operating multiple service types, the NEHR contribution requirement follows the implementation timeline applicable to each service.
Singapore GP clinics must start contributing required health information to NEHR and implement applicable HIA Cybersecurity and Data Security measures by 1 September 2027. Specialist outpatient clinics have a later September 2028 implementation timeline.
What Exactly Must GP Clinics Do by 1 September 2027?
For GP clinics, the HIA deadline is not simply an “NEHR deadline.” There are two major technical workstreams to prepare for:
NEHR contribution
Cybersecurity and Data Security compliance
Both matter.
A clinic could have a system capable of connecting to NEHR while still having weaknesses elsewhere in its IT environment. Likewise, having antivirus, backup, and a firewall does not automatically mean the clinic is ready to meet its NEHR contribution obligations.
Let's look at each requirement separately.
-
The HIA establishes a legal framework for licensed healthcare providers to contribute key patient health information to the National Electronic Health Record (NEHR).
For GP clinics, mandatory contribution begins from 1 September 2027 under the current implementation schedule.
This means clinics need an appropriate Health Information Management System (HIMS) capable of meeting the HIA requirements and connecting securely to NEHR.
MOH states that healthcare providers must use a HIA-compliant HIMS for secure connection and contribution of core health information to NEHR.
What should your clinic check now?
Do not wait until August 2027 to ask whether your existing clinic system is ready.
Find out:
What HIMS or Clinic Management System are you currently using?
Is the system expected to become HIA-compliant?
Can it support NEHR contribution?
Does your clinic already have NEHR access?
Will migration to another HIMS be required?
What patient data may need to be migrated?
Who will manage the technical transition?
How will your wider IT environment connect securely to the system?
Your HIMS provider will typically handle the system-specific NEHR onboarding process.
Advance IT can work on the surrounding IT environment, including devices, accounts, Microsoft 365, network infrastructure, cybersecurity, backups and ongoing IT management, so that securing the clinic does not stop at the HIMS itself.
-
This is the part clinics should not overlook. Under the HIA framework, healthcare providers must meet mandatory Cybersecurity and Data Security (CS/DS) standards.
These requirements cover how health information is stored, accessed, used and shared. MOH developed the CS/DS Essentials in consultation with the Cyber Security Agency of Singapore (CSA), IMDA and PDPC. In practical terms, clinics and healthcares in Singapore should be looking beyond their clinic management software.
Health information may interact with:
clinic desktops and laptops;
employee accounts;
administrator accounts;
servers;
Microsoft 365;
email;
Wi-Fi;
firewalls and network equipment;
shared drives;
backup systems;
remote-access tools;
third-party vendors; and
other applications used by staff.
HIA cybersecurity is therefore an environment-level issue, not just a software issue. This is where an IT readiness assessment becomes valuable.
Advance IT can review the clinic's existing IT environment against the relevant requirements, identify technical gaps and help implement the improvements required to strengthen the clinic's security posture.
-
One of the easiest mistakes is to respond to a compliance deadline by immediately buying more cybersecurity products. Start with the gaps instead.
MOH now provides a Cybersecurity and Data Security Self-Assessment Tool (SAT) designed to help organisations identify areas for improvement against the CS/DS Essentials and HIA Implementation Guide.
A useful assessment should answer questions such as:
Devices: Do you know which computers and devices can access health information?
Accounts: Does every employee have an individual account, and are unnecessary privileges removed?
Network: Is your clinic network properly configured and protected?
Updates: Are operating systems, applications and devices patched consistently?
Malware protection: Are endpoints adequately protected?
Backups: Is important data backed up, and can it actually be restored?
Access: Who has administrator-level access?
Monitoring: Would you know if something suspicious happened?
Incident response: Does the clinic know what to do after a cybersecurity incident?
Vendors: Do you know which third parties can access your systems or health information?
The result should be a clear remediation plan:
Requirement → Current State → Gap → Action → Owner → Deadline. That is much more useful than simply asking, “Are we HIA compliant?”
-
There is now a specific Cyber Essentials for HIA Entities certification scheme.
It is a sub-scheme of Cyber Essentials (2025), co-developed by MOH and CSA specifically for organisations subject to the Health Information Act. CSA provides both the certification documentation and a dedicated self-assessment template for HIA entities.
It is important, however, to distinguish HIA CS/DS compliance from Cyber Essentials certification.
Healthcare providers must comply with the applicable HIA Cybersecurity and Data Security requirements. Cyber Essentials for HIA Entities is a related CSA certification pathway with its own assessment process.
And there is another important distinction: Your IT provider does not award the Cyber Essentials mark.
The certification process is undertaken by independent certification bodies appointed by CSA. The assessment includes desktop review and verification of the organisation's self-assessment by an independent assessor.
-
A self-assessment is useful only if something happens after it. Suppose the assessment identifies:
unsupported operating systems;
weak administrator controls;
incomplete endpoint protection;
inconsistent patching;
missing backups;
untested recovery;
insecure network configurations;
shared user accounts;
undocumented systems; or
inadequate security processes.
The next step is remediation. For a clinic without an internal IT department, coordinating all of these changes can become difficult, particularly when different systems are managed by different vendors.
This is where Advance IT can act as the clinic's IT team, helping translate assessment findings into actual technical changes.
Depending on the environment, that can involve strengthening endpoint security, managing user accounts, improving network protection, reviewing backup arrangements, updating systems, documenting infrastructure and establishing ongoing maintenance.
The objective is simple: Do not enter an independent assessment knowing there are unresolved technical gaps.
-
HIA readiness is not only about preventing incidents. Your clinic also needs to know what happens when an incident occurs.
Under the HIA framework, healthcare providers must assess cybersecurity incidents and data breaches to determine whether they are notifiable.
For a notifiable incident or breach, the current MOH guidance states that an initial notification must be made to MOH within two hours after the incident or breach has been assessed as notifiable. A detailed report must follow within 14 days of the initial notification.
That distinction is important: the two-hour timeline is tied to the assessment that the incident is notifiable, rather than simply two hours from when any IT problem first occurs.
Clinics should therefore establish responsibilities before an incident happens.
Who detects it?
Who contacts the IT provider?
Who assesses the technical impact?
Who determines whether escalation is required?
Who preserves relevant information?
Who coordinates recovery?
An incident response plan sitting unread in a folder is not enough. The people involved need to understand their roles.
-
A backup existing somewhere does not automatically mean a clinic can recover. A more useful question is: If an important system failed today, could we restore what we need? Clinics should understand:
what is backed up;
how frequently backups occur;
where backups are stored;
whether backups are protected;
who monitors failed backup jobs;
how long information is retained; and
whether restoration has been tested.
Advance IT's managed IT approach treats backup as part of ongoing IT operations rather than a one-time installation.
For healthcare organizations, this matters because security is not only about preventing unauthorized access. It is also about maintaining the availability and integrity of important systems and information.
-
Access control is one of the simplest concepts in cybersecurity and one of the easiest to get wrong. Consider a common scenario: “A staff member leaves the clinic. Their Microsoft 365 account is still active. Their computer login remains available. A shared administrator password has not changed. Remote access may still be configured. No sophisticated cyberattack is required for that to become a security problem.”
Clinics should know:
who has access;
what each person can access;
who has administrator privileges;
how new users are onboarded;
how departing employees are offboarded; and
how access is reviewed over time.
For clinics using Advance IT for ongoing managed support, account administration and IT maintenance can form part of a more structured IT management process rather than being handled only when someone remembers to request a change.
-
There is also financial support available for eligible healthcare providers. For Outpatient Medical Service (GP) licensees, the NEHR Connect Grant (NCG) opened on 1 July 2026.
The current grant schedule states:
NCG application deadline: 31 August 2027
Mandatory NEHR contribution: 1 September 2027
NCG quantum for Outpatient Medical Services: S$8,400
MOH also lists EDGE Grant support for eligible healthcare businesses implementing cybersecurity and data-security solutions. This gives clinics another reason to start planning early.
A compliance project may involve multiple vendors, grant applications, system changes, security remediation and NEHR onboarding. Trying to coordinate all of this immediately before September 2027 creates unnecessary operational risk.
Where Advance IT fits
Advance IT's role is on the preparation and remediation side: Advance IT runs the CSA self-assessment with your clinic, identifies and fixes the technical gaps it finds, then hands you to a CSA-appointed certification body audit-ready.
The independent certification body performs the certification assessment and determines the certification outcome. That distinction matters. We help you prepare for the audit. We do not issue the mark.
HIA Readiness Timeline for GP Clinics
If your GP clinic has not started preparing, here is a practical sequence.
Now: Understand Your Current Environment
Identify your HIMS, computers, network, accounts, Microsoft 365 environment, backups, cybersecurity tools and third-party vendors. Confirm your HIMS roadmap for HIA and NEHR.
Next: Run the Gap Assessment
Assess your environment against the applicable HIA CS/DS requirements. If Cyber Essentials for HIA Entities is part of your clinic's cybersecurity pathway, complete the relevant CSA self-assessment and identify the evidence and controls that need attention.
Then: Remediate
Prioritise gaps according to risk. Some may be straightforward configuration changes. Others may require new security controls, network changes, system upgrades or replacement of outdated infrastructure.
Before the Deadline: Verify
Do not assume that installing something means the requirement is solved. Check that controls are implemented, documented and operating as expected. Where pursuing Cyber Essentials certification, prepare the self-assessment and supporting evidence for independent verification by a CSA-appointed certification body.
By 1 September 2027: Be Operationally Ready
For GP / Outpatient Medical Service providers in Batch 1, the goal is not to begin preparation on this date. The goal is to reach it with your NEHR contribution capability and applicable CS/DS measures already in place.
HIA Deadline FAQ
-
No. The deadline depends on the healthcare service.
GP / Outpatient Medical Services are in the September 2027 batch. Specialist Outpatient Medical Services are scheduled for September 2028, while Outpatient Dental services are scheduled for March 2030.
-
GP clinics must be ready to contribute the required health information to NEHR and implement the applicable HIA Cybersecurity and Data Security measures by the September 2027 implementation date.
-
No. NEHR contribution and Cybersecurity and Data Security are separate parts of HIA readiness. Healthcare providers are required to meet mandatory CS/DS standards in addition to their applicable NEHR requirements.
-
Healthcare providers required to contribute to NEHR must use a HIA-compliant HIMS capable of securely connecting to and contributing the required health information to NEHR.
-
Cyber Essentials for HIA Entities is a dedicated sub-scheme of CSA's Cyber Essentials certification, co-developed by MOH and CSA for entities subject to the Health Information Act.
-
No. Cyber Essentials certification is conducted by independent certification bodies appointed by CSA.
Advance IT can support the preparation stage: we run the CSA self-assessment with your clinic, fix the technical gaps it identifies, prepare the environment and supporting evidence, then hand you to the CSA-appointed certification body audit-ready.
The certification body independently performs the assessment and determines the certification outcome.
-
Now is a sensible time to assess readiness.
HIA preparation can involve HIMS changes, NEHR onboarding, cybersecurity remediation, infrastructure upgrades, documentation and coordination with multiple vendors. Starting early provides time to identify and resolve gaps without rushing changes close to the September 2027 deadline.
Don't Treat 1 September 2027 as the Starting Date
The HIA deadline may look distant on a calendar. Operationally, it is much closer.
A clinic/ healthcare firm first has to understand its current environment. Then identify gaps. Then remediate them. Then verify that the controls actually work. At the same time, it may need to coordinate its HIMS and NEHR onboarding. That process is considerably easier when started before the deadline becomes urgent.
Advance IT helps Singapore clinics turn HIA cybersecurity requirements into an actionable IT plan.
For clinics pursuing Cyber Essentials for HIA Entities, our role is equally clear: Advance IT runs the CSA self-assessment with your clinic, fixes the gaps it finds, then hands you to the certification body audit-ready. The independent audit and certification decision remain with a CSA-appointed certification body.
Is Your Clinic Ready for September 2027?
If you are unsure whether your devices, accounts, network, backups and cybersecurity controls meet the required standard, start by finding the gaps.
Talk to Advance IT about an HIA IT readiness assessment.
Singapore IT Support | Managed IT Services | Infrastructure & Cybersecurity
Book a 30-minute consultation.



Verified market data, trend reports, and strategic insights for Singapore business owners making IT decisions in 2026 and beyond.